How to Open Your App to Partners Without Losing Control
How app owners can define partner access, host capabilities and release authority through a governance model their teams can operate.
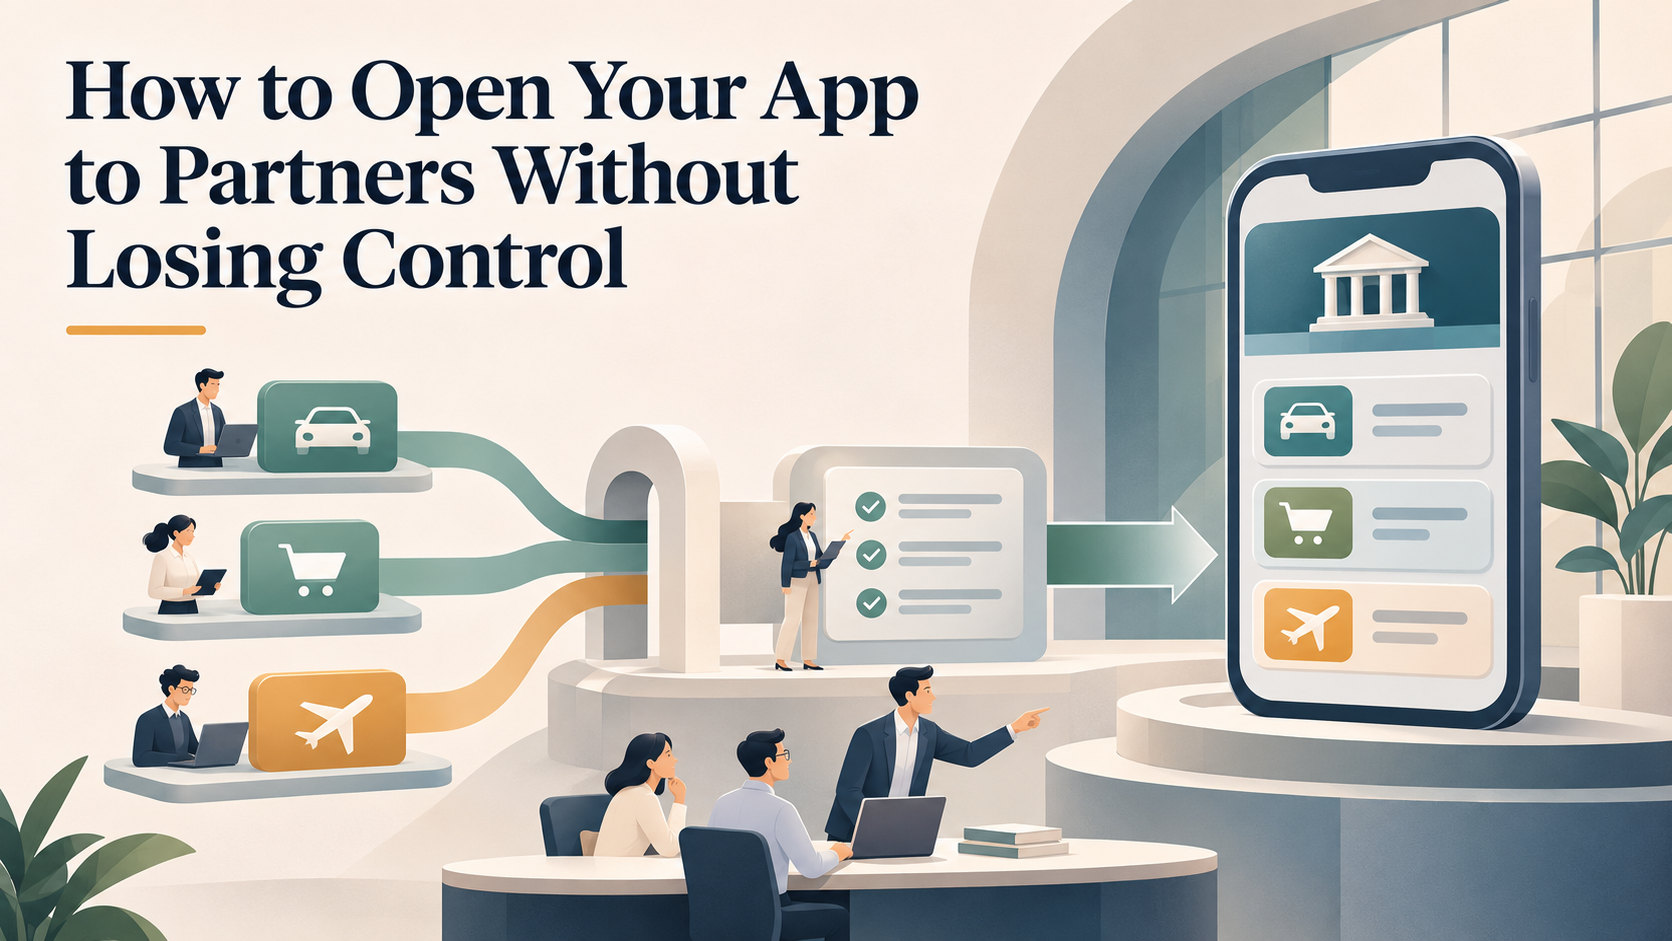
A bank wants to add an inventory-planning service to its business banking app. A software partner can build and maintain the service. The bank's product team sees a useful addition for merchants, while its app team wants a clear answer before development starts: what, exactly, will the partner be allowed to control?
The partner needs room to improve its service. The bank needs authority over participation, access to host capabilities and publication inside its app. Giving every decision to the bank's central team could create a queue. Giving the partner broad access could extend its authority beyond the agreed service.
Consider this bank as an illustrative organisation, not a customer case. Its decision is whether to establish a repeatable way for partners to contribute services under rules the bank can operate. That is the practical purpose of platform governance.
Define the authority being shared
Start with the proposed inventory service. The partner will maintain the planning experience and its business backend. The bank will own the surrounding Host App and decide whether the service belongs in its customer proposition. A named bank team will assess changes affecting that shared environment.
Those responsibilities need several separate decisions. Accepting the partner does not automatically approve every employee it later assigns. Allowing a developer to upload a package does not necessarily give that person publication authority. Approving one service does not establish a need for access to other services or customer records.
An effective arrangement makes these distinctions understandable before either side commits to delivery. The partner knows which work it can advance independently and which requests need a bank decision. The bank can identify the owners of its continuing commitments.
This creates a basis for adding further providers. Each new relationship will still require judgement, but the parties can use an established process instead of negotiating an entirely new operating arrangement around every update.
Put the rules into an operating foundation
In a Mini App model, a service has its own application experience inside the Host App. FinClip provides the Mini App runtime SDK, development tools and management platform. The bank or its implementation partner builds the Host App, business Mini Apps and connected backends; the inventory provider delivers its actual planning service.
FinClip's management capabilities give the enterprise concrete places to apply parts of its governance model. Its documentation describes configurable roles and resource groups for managing access to applications and Mini Apps. These are relevant when deciding which contributors should administer which resources. See the developer-centre user management documentation.
The bank should translate its proposed responsibilities into the configuration it intends to use, then test that configuration with representative accounts. A procurement approval or a partnership agreement cannot establish what a developer account can actually see or change.
For the inventory provider, the practical question is whether its contributors can perform the agreed work on their own service while unrelated resources remain outside their assigned management scope. That is a configuration and verification task, not an assumption to make from a role's name.
Decide which host capabilities a service needs
The provider may ask the Host App for permitted account context so that a merchant can enter its service. That request should have a defined purpose and a clear implementation owner. It should not become a standing entitlement to every capability the bank exposes.
FinClip documents controls for assigning access to registered, host-provided custom APIs and menus. Its API and menu management documentation distinguishes capabilities available directly from those requiring an application and review. Availability varies by environment and product scope.
The bank must still implement the host functions and business authorization behind them. Permission for a Mini App to invoke a host capability is different from permission for a particular merchant to obtain a particular business record. Customer identity, organisation membership and backend checks need their own design.
Suppose the provider later requests transaction history to improve its recommendations. That changes the proposed service boundary. The bank should assess the purpose, necessary information and responsible systems before implementing or granting the additional access. Treating it as an ordinary interface update would conceal a business decision inside a development task.
Review a defined release
The first successful demonstration is only one point in the relationship. The provider will fix defects and propose improvements. The bank needs a release process that lets that work continue while maintaining an identifiable review boundary.
FinClip's Mini App management documentation describes code packages, trial and review versions, publication, removal from publication and version rollback. These mechanisms support a managed application lifecycle. The parties must decide what their review examines and who can make the relevant decisions.
For the inventory service, reviewers should be able to identify the package under consideration, the intended host environment and any change to requested capabilities. The bank's technical team can assess host interactions. The service owner can assess the customer proposition and support readiness. A partner's ability to prepare an update can be broader than its authority to make that update public.
The review also needs to account for work outside the package. A provider might change backend behaviour without submitting a new Mini App version. The operating agreement should identify which service changes require notification or renewed review, and the teams should establish how they will validate those changes. Package approval covers the artefact examined at that time.
Match the review effort to the change
Central control becomes expensive when every request follows the same path regardless of its consequences. A correction to explanatory text and a request for a new host capability should be distinguishable in the operating process.
The bank can define categories using the actual service design. A change within an established interface may follow a routine review. A new capability request may involve the host owner and the relevant business-system owner. A change to the provider's customer offer may require the service sponsor to reconsider support and participation conditions.
These are organisational choices to implement through available roles, permissions and release procedures. Their purpose is to make authority legible. A developer should know where to submit a request, and a reviewer should know what decision they are being asked to make.
Review capacity is part of the investment. If nobody has time or authority to assess capability requests, the ecosystem will either wait or accumulate informal exceptions. Buying management software does not allocate that capacity. The bank needs to fund it alongside the services it expects partners to maintain.
Make intervention workable before it is urgent
Assume an update to the inventory service begins showing inconsistent recommendations. The provider needs to investigate; the bank needs to decide whether new customer access should continue. The operating model should already identify who can authorize intervention and who carries out the technical action.
Different problems call for different responses. Reverting a recently published package may address a client-side regression. It may have little effect when the defect is in an unchanged backend. Withdrawing an entry from a promotional page is also different from removing the Mini App from publication.
The teams should validate the behaviour of their chosen controls, including supported app versions and any already-open sessions. They should establish what customers will see and where assistance remains available. A control is useful when its actual effect matches the response the business needs.
Existing service records require separate attention. Removing access to the application does not reverse actions its backend has already accepted. The provider remains responsible for its service work, while the bank and provider coordinate the agreed assistance route.
Use the same discipline when a relationship ends
A partner can leave for commercial reasons even when its technology works. The bank should be able to stop new participation while handling the remaining service commitments deliberately.
For the inventory provider, that includes developer-account access, application publication, host capability grants and the continuing availability of customer assistance. The relevant teams need to identify which controls they own and confirm the effect of changes in their environment.
There is also a business transition. Merchants may need access to information held by the provider, and support may continue after the app entry closes. The agreed arrangement should name the people and systems responsible. The platform team can coordinate technical withdrawal with that work rather than treating removal as the entire exit process.
Assess governance as part of the growth model
The bank can now evaluate a more useful proposition than simply adding another service. Can it invite a provider, assign an appropriate management scope, assess capability requests, review a release and end participation through a process its teams can maintain?
That process earns its cost when it supports useful services and gives contributors a predictable route to delivery. It may be excessive for a small, static addition with one internal owner. It becomes more relevant as independent contributors and continuing changes become part of the app's business model.
Start with a representative provider and test the proposed responsibilities through real tasks. Where people repeatedly need informal access or exceptional intervention, investigate whether the scope, configuration or decision process needs to change. The result should be a working pattern for collaboration, with clear authority at each boundary.
FAQs
Does opening an app to partners require a public marketplace?
No. A bank can work with selected providers under defined participation rules. A public listing or open developer-registration model is a separate business choice. The technical and operational arrangements should fit the contributors the bank actually intends to support.
Can a partner prepare updates while the bank controls publication?
The intended responsibilities can separate preparation, review and publication. The enterprise should map those responsibilities to the roles and lifecycle controls available in its selected FinClip environment, then verify them with representative accounts and release tasks.
Is Mini App permission management the same as customer authorization?
They address different decisions. A Mini App may receive permission to invoke a host-provided capability, while the host and business backend still need to determine what the current customer is entitled to do or see. Both boundaries require implementation and testing.
Does package approval cover every subsequent service change?
A reviewed package identifies one application artefact. Backend behaviour, content and operational arrangements can change separately. The platform owner and provider should define which changes need notification, validation or another approval and assign responsibility for that work.
How should an enterprise evaluate FinClip for ecosystem governance?
Use a representative partner service and test contributor access, resource scope, required host capabilities and release responsibilities. Include intervention and withdrawal tasks in the assessment. Confirm the relevant capabilities against the proposed product environment, version and project scope.
Discuss the rules your app needs to operate
Bring a representative partner service and its proposed access and release responsibilities to FinClip. We can discuss how the runtime, development tools and management platform could support the ecosystem your organisation intends to run.